What We Deliver
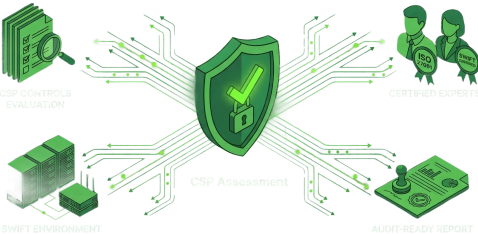
CSP Control Validation
Independent assessment of your implementation against SWIFT’s mandatory and advisory controls, including software integrity, access management, and environment segregation.

Gap Analysis & Remediation Planning
Detailed identification of compliance gaps with prioritized remediation steps, tailored to your infrastructure and risk profile.

Evidence Review & Documentation Support
Guidance on preparing audit-ready evidence for each control, including screenshots, logs, policies, and configuration files.

Attestation Preparation
Support for completing the SWIFT CSP attestation form, including advisory on self-attestation vs. independent assessment pathways.

Technical & Governance Advisory
Recommendations on firewall rules, connector hardening, backup encryption, and governance alignment with ISO 27001 standards.

Service Highlights
Delivered by ISO 27001 Lead Auditors and SWIFT-certified engineers
Covers all 3 CSP control objectives: Secure Your Environment, Know & Limit Access, Detect & Respond
Includes remote and on-site assessment options
Why Choose Us?

Proven track record across MENA, South Asia, and Africa

Deep expertise in SWIFT infrastructure, cybersecurity, and regulatory compliance

Structured reporting with executive summaries and technical annexes
